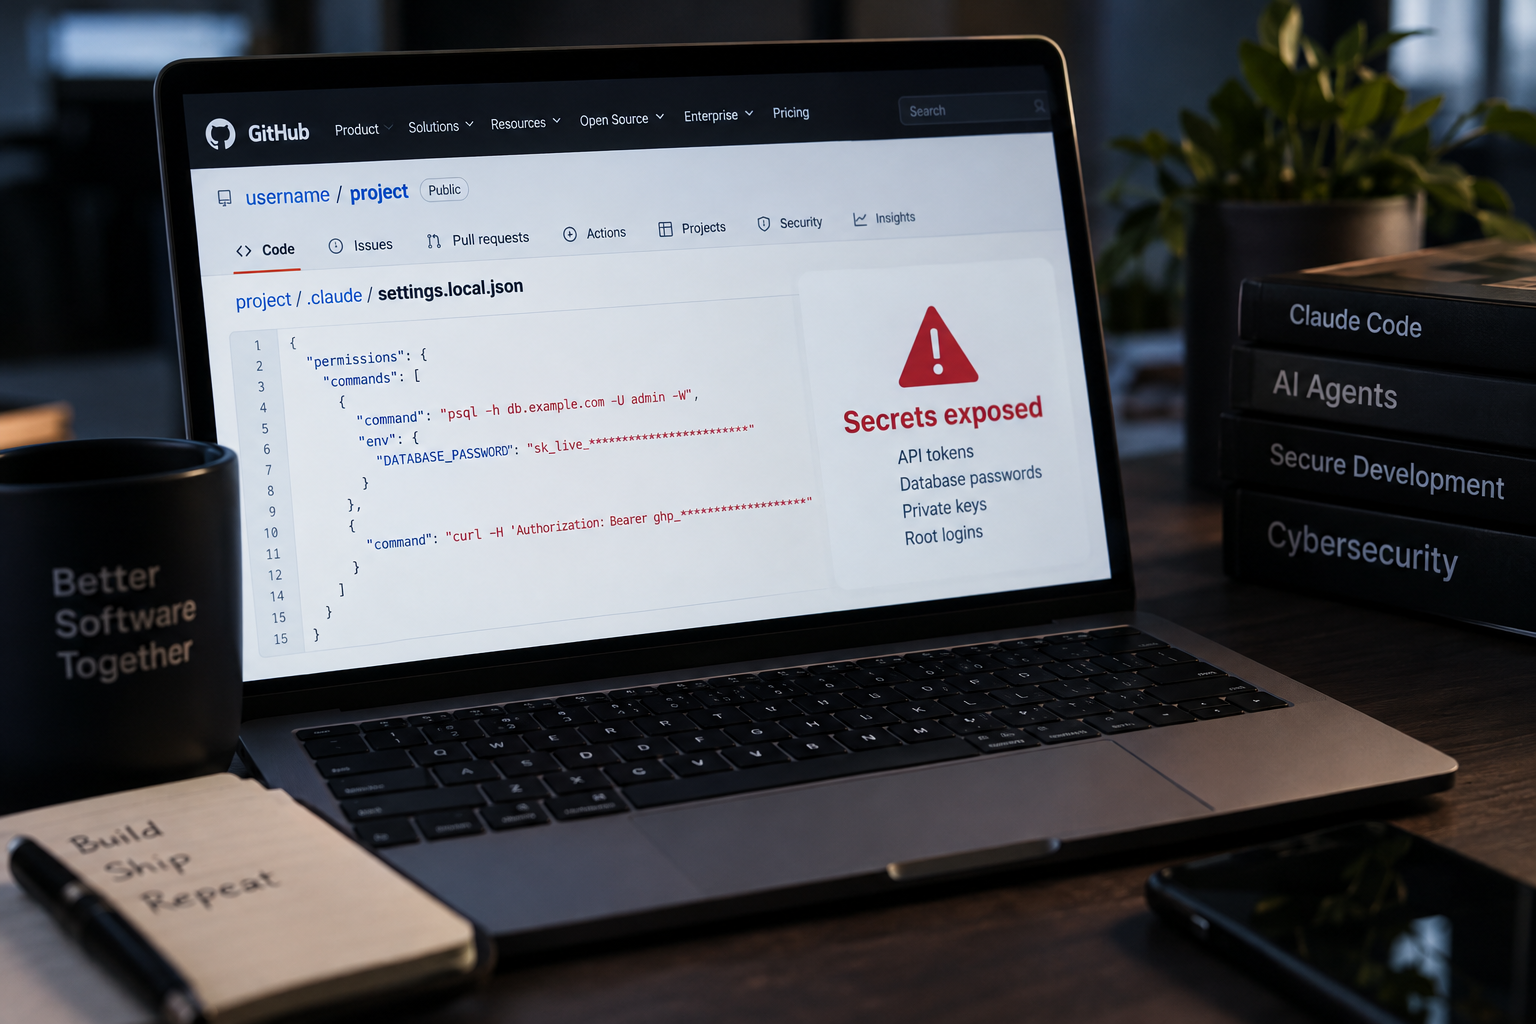
Claude Code is exposing sensitive information on public GitHub repositories, and the problem stems from a settings file that many developers never think about. Security researchers at Apiiro say they found thousands of secrets, including database passwords, API tokens and root logins, inside Claude Code settings files that had been uploaded to public code repositories.
How does Claude Code expose secrets in settings files?
The leak comes from how the tool handles approval for automated shell commands. When a user selects “Yes, and don’t ask again” to approve a command, Claude Code saves that choice as a rule in a local file called “.claude/settings.local.json.” Sometimes the rule is stored as a pattern. Often, though, the command is written into the file exactly as entered, including any sensitive information it contains.
On a single developer’s machine, that file poses little risk, as long as the machine itself stays secure. Anthropic’s Claude Code documentation says the file is added to a developer’s global .gitignore list, which typically keeps it from being shared. The catch is that the protection lives at the global level and is not reflected in each repository. If a project is cloned to another machine, or a folder later becomes a repository, the file can be uploaded by accident. Apiiro says Claude Code itself will sometimes commit changes to the settings file without any input from the user.
Can secrets be removed once a settings file is public?
Apiiro’s researchers found more than 100,000 cases in which the local settings file had been uploaded to a public GitHub repository. Of those, about 1,100 came from 63 different organizations and contained secrets such as public API tokens, database passwords or private keys. Removing a file from a repository does not erase the secrets. They can persist in forks of the original project, and a GitHub user who copied the project before the cleanup may still have them.
The issue is not new. A bug report flagged the problem in August 2025. Other reports said the sensitive file was not always added to the .gitignore list, or that Claude Code could write the sensitive commands to a different file that git did not protect. All of those reports were closed without action after 60 days of inactivity.
The developers are now responding in public. In a comment thread on Hacker News over the weekend, Claude Code’s Boris Cherny said the team is “looking into what we can do to prevent this.” He also said the settings files should almost never be checked into a user’s git source control, and that cases like these seem to arise only when “the files were manually created and checked in.”
Cherny suggested that users try Claude Code’s auto mode in the meantime. Auto mode uses classifiers to route “routine permission prompts” automatically, so users do not have to maintain what he called “finicky allow/deny lists” by hand. Another user then pointed out that sensitive commands can still be saved to settings files in auto mode. Cherny called that a “good catch” and said the team is “thinking through what we can do to improve this.”
Do secret scanners catch leaked Claude Code secrets?
He also urged users to rely on secret scanners, tools that search files for sensitive information and remove it. Cherny said the team has considered building that kind of scanning into Claude Code. Those tools are not foolproof, however. Apiiro found that 215 of the roughly 1,100 public secrets it identified in Claude Code settings files were missed by two popular scanners, gitleaks and TruffleHog.
Claude Code is not the only AI agent that has leaked sensitive information by accident. Meta suspended the sharing feature on its Muse agent after security researchers found that the URLs for shared content could be easily guessed.
This article was written with the assistance of AI.
News Factory APP - agentic news to boost your SEO & AEO.